Filed under verglos.
Every note is attached to a product, a scan, or a real operational pattern we watched play out in the field. We publish when we have something specific to say — never on a content calendar.
Filtered notes
Verglos · Architecture
AI-authorship provenance, explained
Why probable AI authorship can be useful review context without becoming a vulnerability label, blame mechanism, or substitute for code evidence.
Verglos · Design note
The local sandbox verification concept behind Verglos
A design note for bounded local finding verification, including what exists in Verglos alpha and what still has to be built safely for review.
Verglos · Product proposal
Signed evidence artifacts are the proposed Studio wedge
A product-design note on portable, signed security summaries, with Verglos' unshipped status and trust requirements stated directly for agencies.
Verglos · research note
Slopsquatting in 2026: the numbers that matter
What the primary package-hallucination study measured, what it did not measure, and how JavaScript developers can reduce installation risk before install.
Verglos · Release note
Verglos 2.0 alpha: scanner today, evidence direction next
The honest boundary of Verglos 2.0.0-alpha.1: a functional local scanner, command shells for hunt and attest, and a roadmap that is not yet product truth.
Verglos · Product proposal
The proposed Verglos Free, Pro, Studio, and Enterprise model
A transparent Verglos product-model draft that separates the local alpha from unbuilt paid tiers and avoids invented prices or entitlements.
Verglos · Comparison
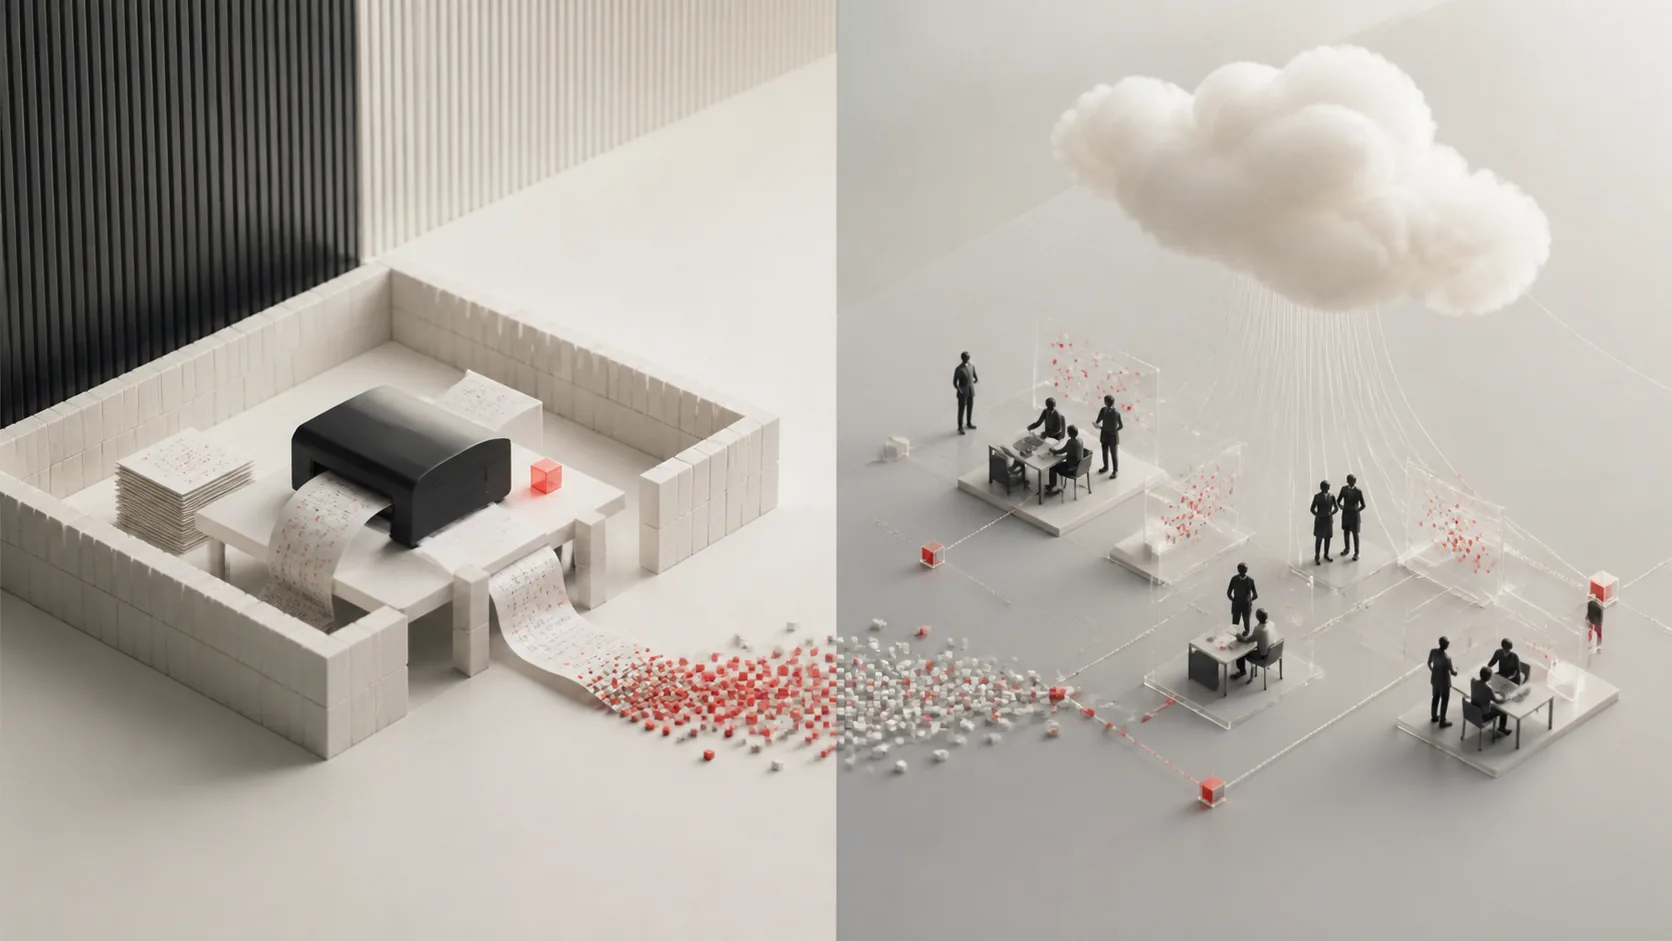
Verglos vs cloud SAST: the trust-model tradeoff
A comparison of Verglos local scanning and hosted application-security platforms based on workflow, context, governance, and evidence needs.
Verglos · Product principle
What Verglos 2.0 alpha refuses
Four product boundaries for Verglos: no autonomous attacks, no cloud requirement for scanning, no compliance theater, and no roadmap passed off as shipping.
Verglos · Positioning
Why Verglos refuses the XBOW lane
XBOW and Verglos address different security jobs: authorized autonomous offensive testing versus a narrow local scanning and evidence direction.
Verglos · field guide
Verglos on the CLI, with coding agents, and in CI
The supported Verglos local scan path and conservative ways to place it around agent and CI workflows without inventing integrations or claims.
Verglos · Product principle
Why Verglos will not ship an attacking agent
The authorization, reproducibility, and trust reasons Verglos separates local evidence work from autonomous offensive testing in the current alpha.
Verglos · Research
Eight patterns AI-assisted code keeps producing
Eight reviewable vulnerability shapes that recur in fast-built JavaScript and TypeScript, plus the control that should catch each one in review.
Verglos · Research
What our 300-repository TS/JS scan did and did not show
A corrected account of the Verglos scan campaign, its published artifacts, its 57.7% high-or-critical result, and the limits on interpreting scanner output.
Verglos · Comparison
Verglos alongside Snyk, GitHub, Semgrep, Socket, and Gitleaks
A capability-bound comparison showing where a narrow local alpha scanner may complement established code, dependency, and secret-security tools.
Verglos · thesis
The security evidence layer for AI-built software
Why AI-assisted software needs reviewable security records, and which parts of Verglos' evidence model exist for builders and teams in alpha today.
Verglos · Field note
Responsible disclosure when a scan finds a live credential
A conservative workflow for containment, private outreach, rotation, patch verification, and delayed publication after a scanner finds a possible live secret.