Journal
Verglos · Comparison
Aug 20, 2026
2 min read
By Top Notchh Team
Reviewed Sep 1, 2026
Sources: externally verified
Verglos vs cloud SAST: the trust-model tradeoff
A comparison of Verglos local scanning and hosted application-security platforms based on workflow, context, governance, and evidence needs.
In brief
- Local and hosted scanners optimize for different trust and workflow requirements.
- Cloud platforms can add centralized context and governance; local tools reduce required source sharing.
- Verglos is a narrow alpha scanner, not a replacement for a mature AppSec platform.
Local scanners and cloud application-security platforms are not interchangeable versions of the same architecture. The right choice depends on which trust boundary and operating model a team needs.
What hosted platforms can provide
A hosted platform can maintain organization-wide inventory, run checks continuously, connect findings to repositories and pull requests, centralize policies, route ownership, and preserve security-team workflow. GitHub documents code scanning, dependency review, secret protection, and organization-level security features within its platform. Semgrep offers both local community scanning and a managed AppSec platform.
Those capabilities are valuable when a security team must govern many repositories. They also require careful review of what code, metadata, diffs, and findings the service processes and retains.
What a local scanner can provide
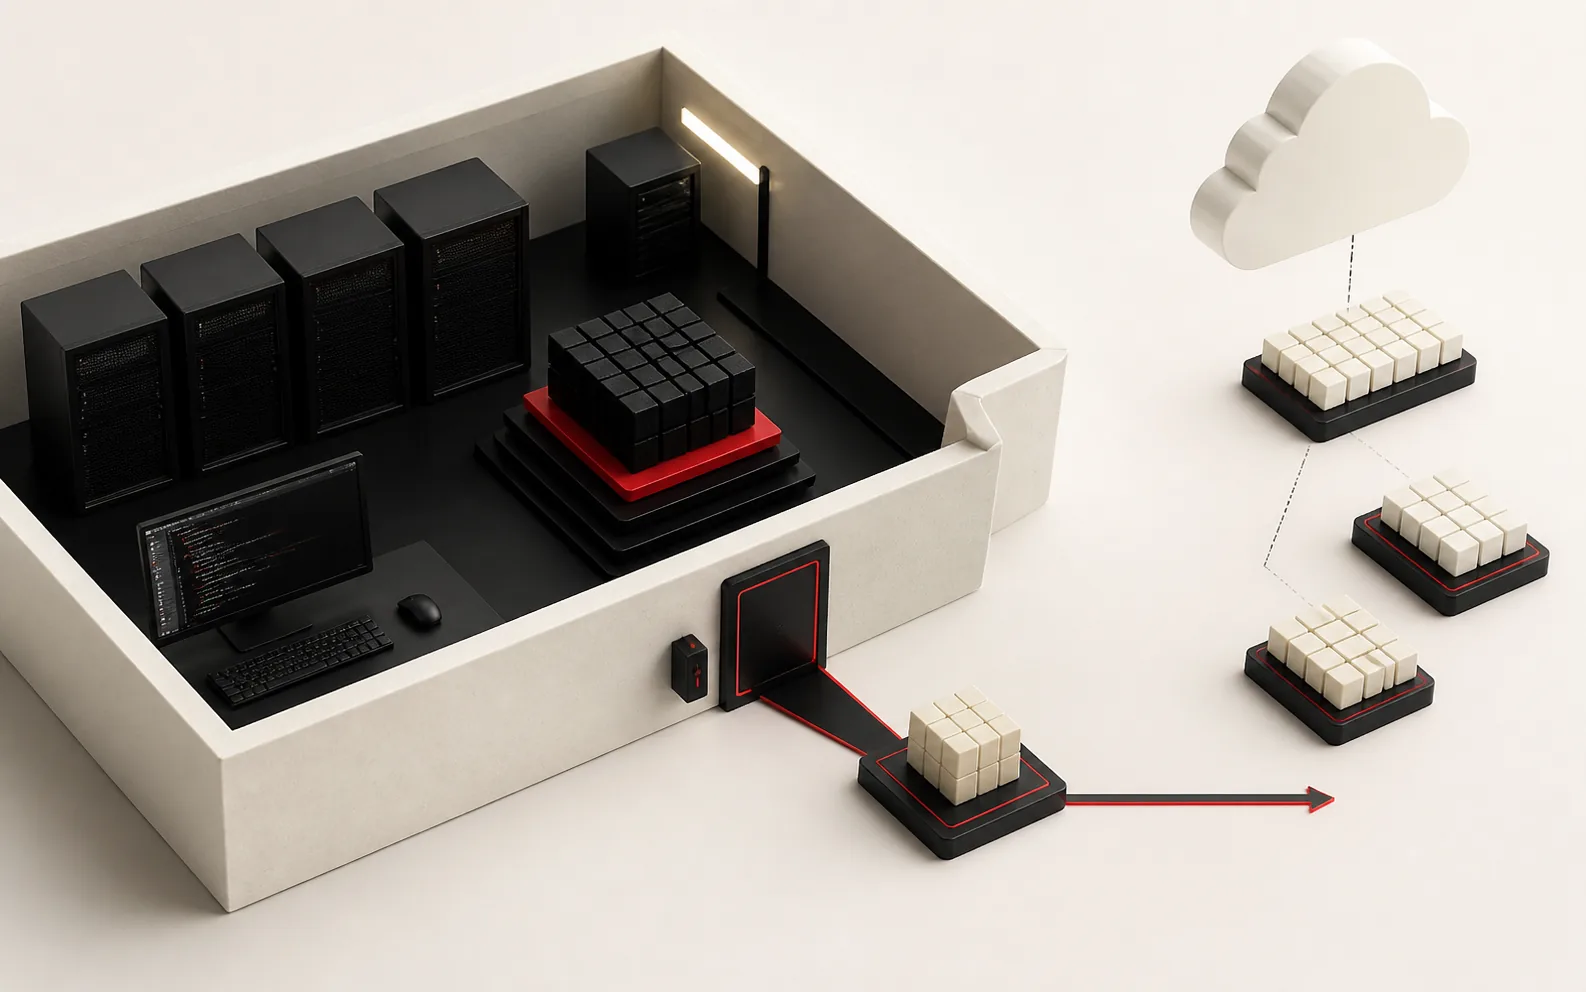
A local-first tool can run without granting a vendor repository access and can keep reports beside the project. It is easy to try on an unconnected checkout and can fit environments where source sharing is constrained.
Local does not mean zero trust. Package installation, rule updates, telemetry, subprocesses, report storage, and the machine itself still matter. Teams should inspect the tool and its network behavior rather than rely on a label.
Where Verglos fits
Verglos currently offers a local scanner focused on JavaScript and TypeScript. It does not provide the organization-wide inventory, workflow breadth, language coverage, or mature governance surfaces of established platforms. Its hunt and attest directions are not shipped in 2.0.0-alpha.1.
That makes the current comparison practical: use Verglos where its local rules and reports add useful coverage, and keep platform tools where they solve broader operational needs. Running more than one scanner can also create duplicated findings and policy conflicts, so teams should define ownership and deduplication.
The tradeoff is not “private versus insecure” or “modern versus legacy.” It is local custody and narrow scope versus centralized context and operations, evaluated against the team's actual threat model.
Evidence ledger
Sources and verification
- Verglos CLI repositoryTop Notchh Solutions · canonical · checked Sep 1, 2026
- GitHub security featuresGitHub Docs · reference · checked Sep 1, 2026
- Semgrep Community EditionSemgrep · reference · checked Sep 1, 2026